
A vulnerability in the Netwrix Auditor software can be exploited to execute arbitrary code on affected devices.
Bishop Fox discovered a vulnerability in the Netwrix Auditor software that can be exploited by attackers to execute arbitrary code on affected devices.
Netwrix Auditor is a an auditing software that allows organizations to monitor their IT infrastructure, it is currently used by more than 11000 organizations worldwide.
The vulnerability is an insecure object deserialization issue that allows an attacker to execute arbitrary code with the privileges of the vulnerable service.
“This issue is caused by an unsecured .NET remoting port accessible on TCP port 9004.” reads the advisory published by Bishop Fox. “An attacker can use this issue to achieve arbitrary code execution on servers running Netwrix Auditor. Since this service is typically executed with extensive privileges in an Active Directory environment, the attacker would likely be able to compromise the Active Directory domain.”
An attacker can exploit the flaw to achieve remote code execution on servers by submitting arbitrary objects to the application through this service.
The experts pointed out that Netwrix Auditor services would be running with a highly privileged account, which could lead to full compromise of the Active Directory environment.
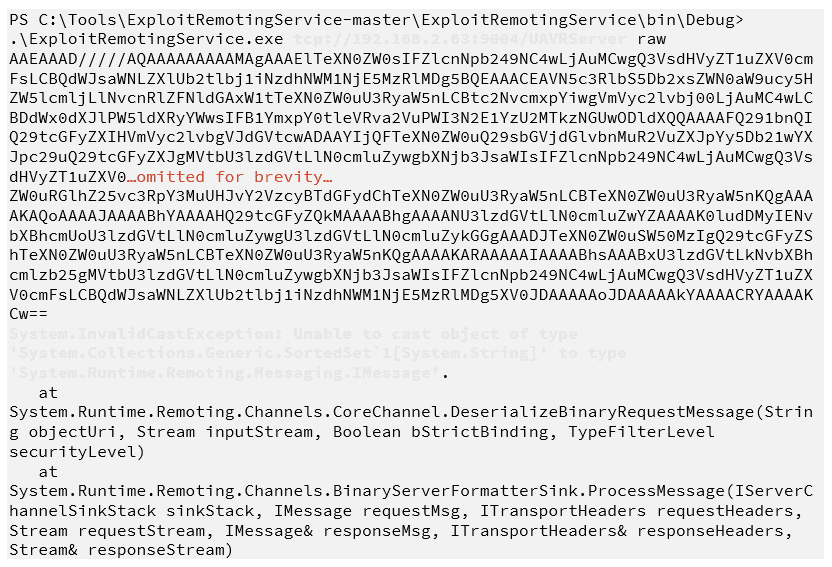
“The ExploitRemotingService tool was then used to send the serialized object to the UAVRServer service over .NET remoting. The resulting exception was an indicator that the payload was executed successfully” continues the advisory.

“Since the command was executed with NT AUTHORITY\system privileges, exploiting this issue would allow an attacker to fully compromise the Netwrix server.”
Netwrix addressed the flaw with the release of the software verision 10.5 on June 6, 2022.
Update July 19, 2022
“Upon receiving the vulnerability report from Jordan Parkin of Bishop Fox, the Netwrix development team worked diligently to remediate it. On June 6, 2022, Netwrix released Netwrix Auditor 10.5 which included a fix for this vulnerability, and published a security advisory to its customers advising them of the risk and the need to upgrade. Netwrix thanks Mr. Parkin for his collaboration and coordinated disclosure of this vulnerability. Customers requiring assistance deploying Netwrix Auditor 10.5 should contact the support team via the customer web portal or by phone in the US at +1.888.638.9749.” reads a statement issued by the company.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Netwrix Auditor)
[adrotate banner=”5″]
[adrotate banner=”13″]


