The Eleven11bot botnet has infected over 86,000 IoT devices, mainly security cameras and network video recorders (NVRs).
Researchers from Nokia Deepfield Emergency Response Team (ERT) discovered a new botnet named Eleven11bot that has already infected over 86,000 IoT devices. Most infected devices are security cameras and network video recorders (NVRs), which are used to launch DDoS attacks.
“On 26 Feb 2025, the Deepfield Emergency Response Team (ERT) identified a significant new Distributed Denial-of-Service (DDoS) botnet, now tracked under “Eleven11bot.” Primarily composed of compromised webcams and Network Video Recorders (NVRs), this botnet has rapidly grown to exceed 30,000 devices. Its size is exceptional among non-state actor botnets, making it one of the largest known DDoS botnet campaigns observed since the invasion of Ukraine in February 2022.” wrote Nokia security researchers Jérôme Meyer.“Eleven11bot has targeted diverse sectors, including communications service providers and gaming hosting infrastructure, leveraging a variety of attack vectors. Attack intensity has varied widely, ranging from a few hundred thousand to several hundred million packets per second (pps). Public forums report sustained attack campaigns causing service degradation lasting multiple days, some of which remain ongoing.”
GreyNoise researchers who also monitored the botnet discovered that 96% of IPs are genuine, and 61% (636 of 1,042) originate from Iran. GreyNoise flagged 305 IPs as malicious, the researchers pointed out that the surge follows new U.S. sanctions on Iran.
“Following Deepfield’s findings, Censys provided GreyNoise with a list of 1,400 IPs that appear to be linked to Eleven11bot due to the configuration of the endpoint devices and the banners matching what Deepfield identified in their research. GreyNoise has observed 1,042 IPs actively hitting our sensors in the past 30 days.” states GreyNoise.
GreyNoise data suggests the botnet is expanding its reach through brute-force attacks, exploiting weak IoT passwords, and targeting VStarcam devices with hardcoded credentials. It also scans for exposed Telnet and SSH ports on vulnerable hardware. So far, 305 IP addresses have been identified as actively engaging in malicious activity linked to the botnet.
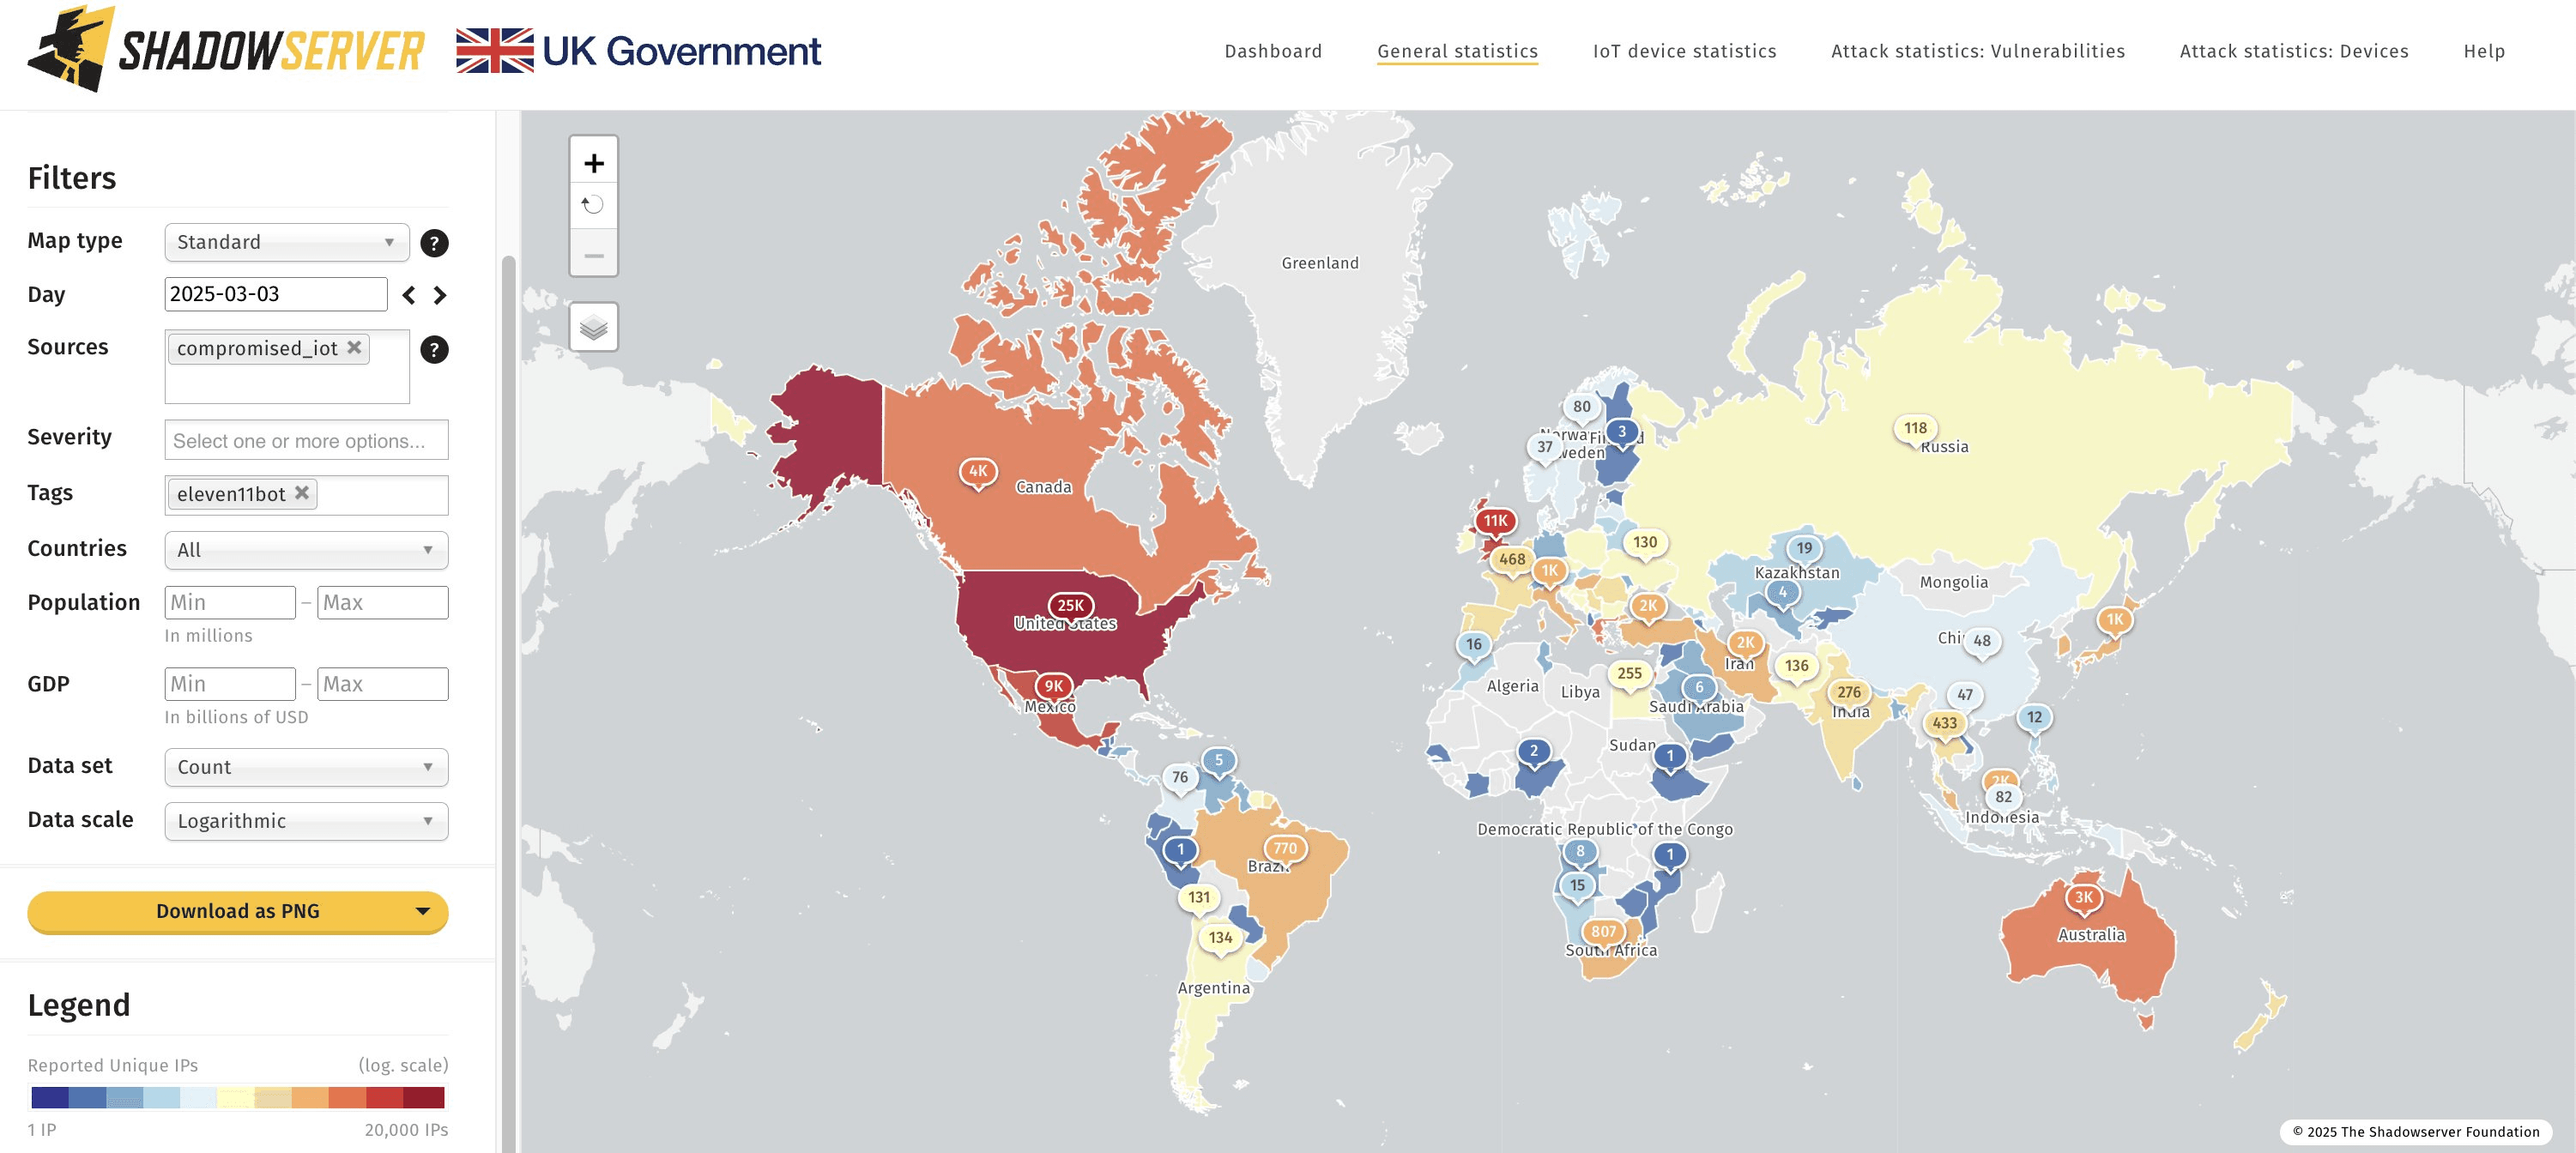
Researchers at Shadowserver Foundation are also monitoring the botnet and reported that they spotted approximately 86,400 devices infected by the Eleven11bot bot. Most of the infected devices are in the US (24.700) and the United Kingdom (10.800).
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, botnet)