Security Affairs
OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Nodersok malware delivery campaign relies on advanced techniques

Microsoft researchers observed a campaign delivering malware, dubbed Nodersok, relying on advanced techniques and elusive network infrastructure. Microsoft experts observed a malware campaign, tracked as Nodersok, relying on advanced techniques and elusive network infrastructure. Microsoft uncovered the campaign in mid-July when noticed patterns in the anomalous usage of MSHTA.exe. Nodersok abuse of legitimate tools also […]

Nodersok campaign

Microsoft researchers observed a campaign delivering malware, dubbed Nodersok, relying on advanced techniques and elusive network infrastructure.

Microsoft experts observed a malware campaign, tracked as Nodersok, relying on advanced techniques and elusive network infrastructure. Microsoft uncovered the campaign in mid-July when noticed patterns in the anomalous usage of MSHTA.exe.

Nodersok abuse of legitimate tools also called living-off-the-land binaries (LOLBins). Researchers observed threat actors dropping two legitimate tools onto the infected machines, namely Node.exe, the Windows implementation of the popular Node.js framework, and WinDivert, a network packet capture and manipulation utility.

“It’s not uncommon for attackers to download legitimate third-party tools onto infected machines (for example, PsExec is often abused to run other tools or commands).” reads the analysis published by Microsoft. “However, Nodersok went through a long chain of fileless techniques to install a pair of very peculiar tools with one final objective: turn infected machines into zombie proxies.”

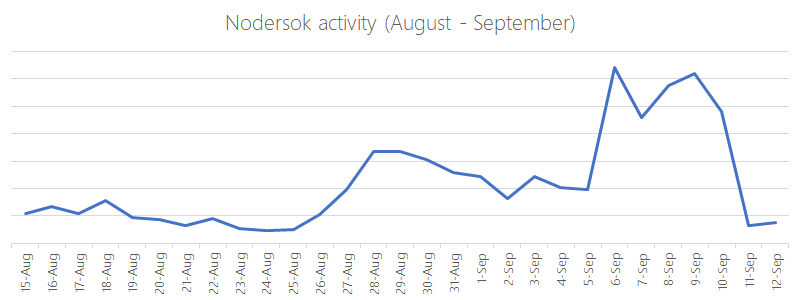
The Nodersok campaign has already infected thousands of machines in the last several weeks. Most of the victims are located in the United States and Europe, they are predominantly consumers. About 3% of the infected systems belong to organizations in different sectors, including education, professional services, healthcare, finance, and retail.

Nodersok campaign

The attack chain starts when the users run an HTML Application (HTA) that is delivered likely through compromised advertisements. The JavaScript code in the HTA file downloads a second state component that launches a Powershell.

The Powershell command downloads additional components. One of the second-stage instances of PowerShell downloads the legitimate node.exe tool, while another drops WinDivert packet capture library components.

Another PowerShell component runs a shellcode to use WinDivert for the filtering and modification of certain outgoing packets.

The final payload turns the infected machine into a proxy.

The attackers leverage lksktWinDivert tool is used to intercept packets sent out to initiate a TCP connection and modify them in a manner that likely benefits the attackers.

“Both the distributed network infrastructure and the advanced fileless techniques allowed this campaign fly under the radar for a while, highlighting how having the right defensive technologies is of utmost importance in order to detect and counter these attacks in a timely manner.” Microsoft concludes.

“If we exclude all the clean and legitimate files leveraged by the attack, all that remains are the initial HTA file, the final Node.js-based payload, and a bunch of encrypted files. Traditional file-based signatures are inadequate to counter sophisticated threats like this.”

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Nodersok, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]