
Security researchers at Arbor Networks have discovered a threat actor targeting financial institutions in Japan using the Panda Banker banking malware (aka Zeus Panda, PandaBot).
Panda Banker was first spotted 2016 by Fox-IT, it borrows code from the Zeus banking Trojan.
In November 2017, threat actors behind the Zeus Panda banking Trojan leveraged black Search Engine Optimization (SEO) to propose malicious links in the search results. Crooks were focused on financial-related keyword queries.
The main feature of the Panda Banker is the stealing of credentials and account numbers, it is able to steal money from victims by implementing “man in the browser” attack.
The Panda Banker is sold as a kit on underground forums, the variant used in the last attacks against Japan if the version 2.6.6 that implements the same features as the previous releases.
“A threat actor using the well-known banking malware Panda Banker (a.k.a Zeus Panda, PandaBot) has started targeting financial institutions in Japan.” reads the analysis published by Arbor Networks.
“Based on our data and analysis this is the first time that we have seen Panda Banker injects targeting Japanese organizations.”
An interesting aspect of this campaign targeting Japan is that none of the indicators of compromise (IOC) was associated with previous attacks.
The threat actor delivered the banking trojan through malvertising, victims were redirected to the domains hosting the RIG-v exploit kit.
Crooks leveraged on multiple domains and C&C servers, but at the time of the analysis, only one of them was active. The unique active domain hillaryzell[.]xyz was registered to a Petrov Vadim and the associated email address was yalapinziw@mail.ru.
The campaign that hit Japan also targeted websites based in the United States, search engines, and social media sites, an email site, a video search engine, an online shopping site, and an adult content hub.
“The threat actor named this campaign “ank”.” continues the analysis. “At the time of research, the C2 server returned 27 webinjects that can be broken down into the following categories:
- 17 Japanese banking web sites mostly focusing on credit cards
- 1 US based web email site
- 1 US based video search engine
- 4 US based search engines
- 1 US based online shopping site
- 2 US based social media sites
- 1 US based adult content hub”
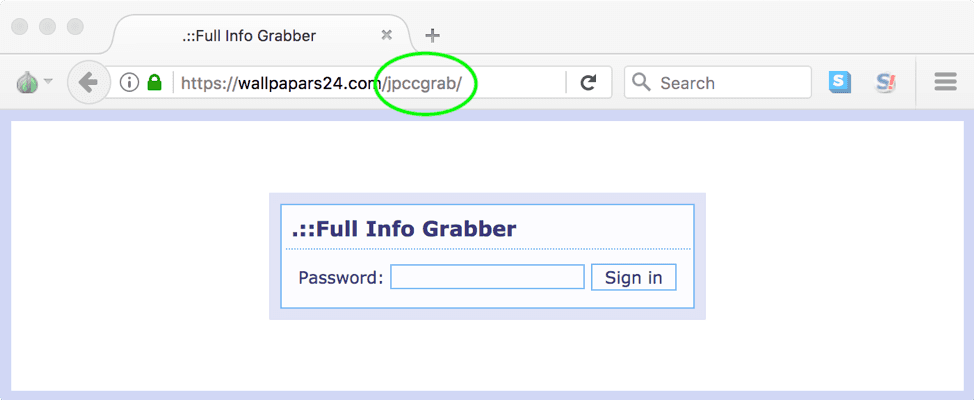
The webinjects employed in this campaign leverage the Full Info Grabber automated transfer system (ATS) to capture user credentials and account information.

| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Banking Trojan, Panda Banker)
[adrotate banner=”5″]
[adrotate banner=”13″]


