
Experts at Kaspersky Lab have linked a series of cyber attacks started in 2001 to a single threat actor called the Poseidon Group.
Experts at Kaspersky Lab have identified a single threat actor behind a long-known campaign of cyberattacks financially motivated.
The group of hackers identified by Kaspersky dubbed Poseidon Group attempts to extort money to corporate victims.
The researchers believe the group has been active since 2001, the hackers developed malicious code to infect systems that use English and Portuguese settings.
“During the latter part of 2015, Kaspersky researchers from GReAT (Global Research and Analysis Team) got hold of the missing pieces of an intricate puzzle that points to the dawn of the first Portuguese-speaking targeted attack group, named “Poseidon.” The group’s campaigns appear to have been active since at least 2005, while the very first sample found points to 2001″ Kaspersky wrote in a post .
The attackers spread the malware through spear-phishing emails, the messages include malicious office documents as an attachment. Once the malware compromises a system in the target network, it tries to map its topology searching for sensitive data to exfiltrate.
In order to map the network and make lateral movements, the malware searches for all administrator accounts on both the local machine and the network.
The Poseidon group not only steal data from victims, it tries to use the information gathered to blackmail victims into contracting the hacking crew.
“The information exfiltrated is then leveraged by a company front to blackmail victim companies into contracting the Poseidon Group as a security firm,” continues Kaspersky. ” Even when contracted, the Poseidon Group may continue its infection or initiate another infection at a later time, persisting on the network to continue data collection beyond its contractual obligation.”
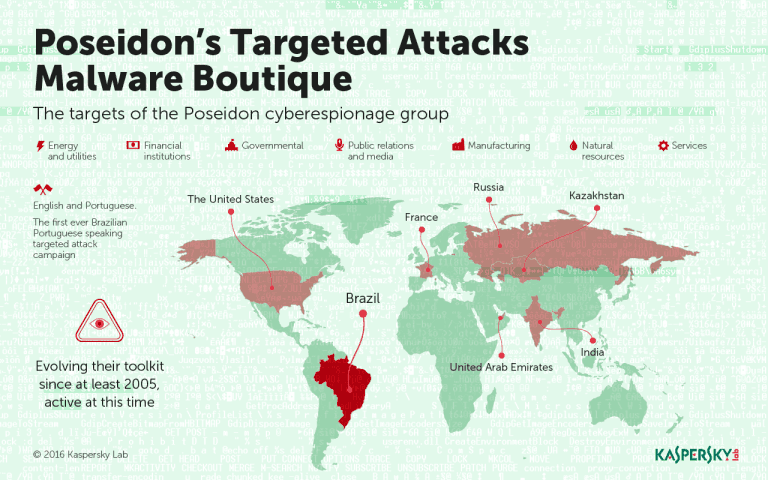
Experts at Kaspersky revealed that at least 35 companies have been targeted by the Poseidon Group, including organizations in banking, government, telecommunications, manufacturing and energy, and media industries.

This the first time that a security firm link the Poseidon Group’s attacks to a single threat actor.
“We noticed that several security companies and enthusiasts had unwittingly reported on fragments of Poseidon’s campaigns over the years. However, nobody noticed that these fragments actually belonged to the same threat actor.” states the report from Kaspersky
“By carefully collecting all the evidence and then reconstructing the attacker’s timeline, we found that it was actually a single group operating since at least 2005, and possible earlier, and still active on the market,”
Kaspersky informed victims of the attacks and disclosed the indicators of compromise to allow firms to identify the threat.
(Security Affairs – Poseidon Group, cybercrime)


