Security Affairs
U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Expert released DOS Exploit PoC for Critical Windows RDP Gateway flaws

Danish security researcher Ollypwn has released DOS exploit PoC for critical vulnerabilities in the Windows RDP Gateway. The Danish security researcher Ollypwn has published a proof-of-concept (PoC) denial of service exploit for the CVE-2020-0609 and CVE-2020-0610 vulnerabilities in the Remote Desktop Gateway (RD Gateway) component on Windows Server (2012, 2012 R2, 2016, and 2019) devices. A Remote Desktop Gateway server is typically […]

RDP Gateway

Danish security researcher Ollypwn has released DOS exploit PoC for critical vulnerabilities in the Windows RDP Gateway.

The Danish security researcher Ollypwn has published a proof-of-concept (PoC) denial of service exploit for the CVE-2020-0609 and CVE-2020-0610 vulnerabilities in the Remote Desktop Gateway (RD Gateway) component on Windows Server (2012, 2012 R2, 2016, and 2019) devices.

https://twitter.com/ollypwn/status/1220481667539841024

A Remote Desktop Gateway server is typically is located in a corporate or private network and acts as the gateway into which RDP connections from an external network connects through to access a Remote Desktop server (Terminal Server) located on the corporate or private network.

“A remote code execution vulnerability exists in Windows Remote Desktop Gateway (RD Gateway) when an unauthenticated attacker connects to the target system using RDP and sends specially crafted requests. This vulnerability is pre-authentication and requires no user interaction. An attacker who successfully exploited this vulnerability could execute arbitrary code on the target system. An attacker could then install programs; view, change, or delete data; or create new accounts with full user rights.” reads the advisories published by Microsoft.

“To exploit this vulnerability, an attacker would need to send a specially crafted request to the target systems RD Gateway via RDP.”

Microsoft addressed the two vulnerabilities with the release of the January Patch Tuesday.

The PoC code released by the researcher also includes a built-in scanner for checking if a host is vulnerable to both CVE-2020-0609 and CVE-2020-0610 issues.

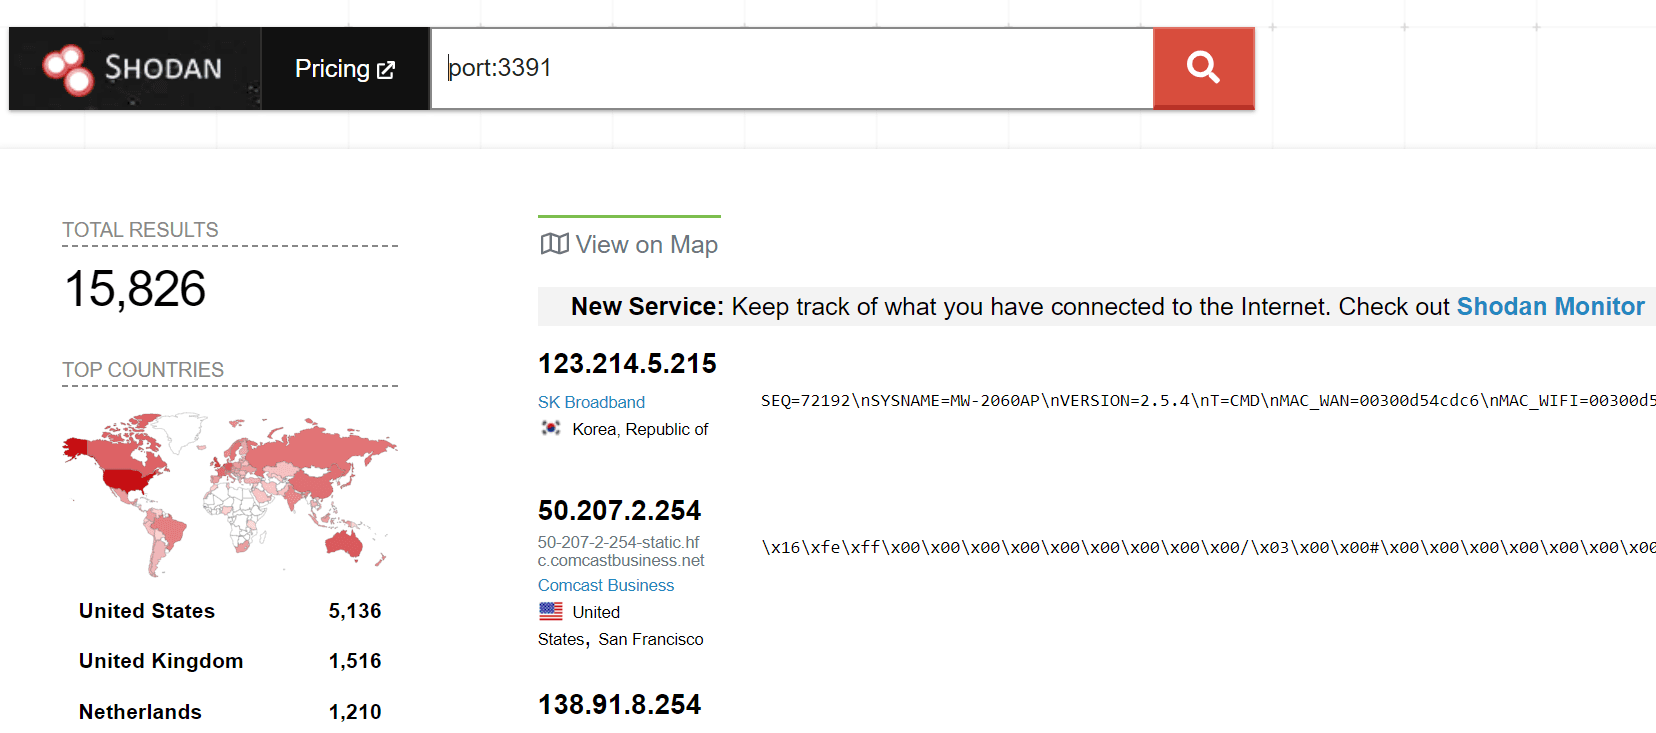
Scanning for vulnerable RDP Gateway servers with Shodan, the search engine has found over 15,500.

RDP Gateway

Experts suggest securing vulnerable RDP Gateway servers by installing the security updates ([1], [2]) released by Microsoft.

To mitigate the risk of exploitation it is possible to disable UDP ore protect access to UDP port.

“Simply disabling UDP Transport, or firewalling the UDP port (usually port 3391) is sufficient to prevent exploitation,” explained the popular researcher Marcus Hutchins.

Microsoft is not aware of attacks in the wild exploiting the above vulnerabilities.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – RDP Gateway, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]