Security Affairs
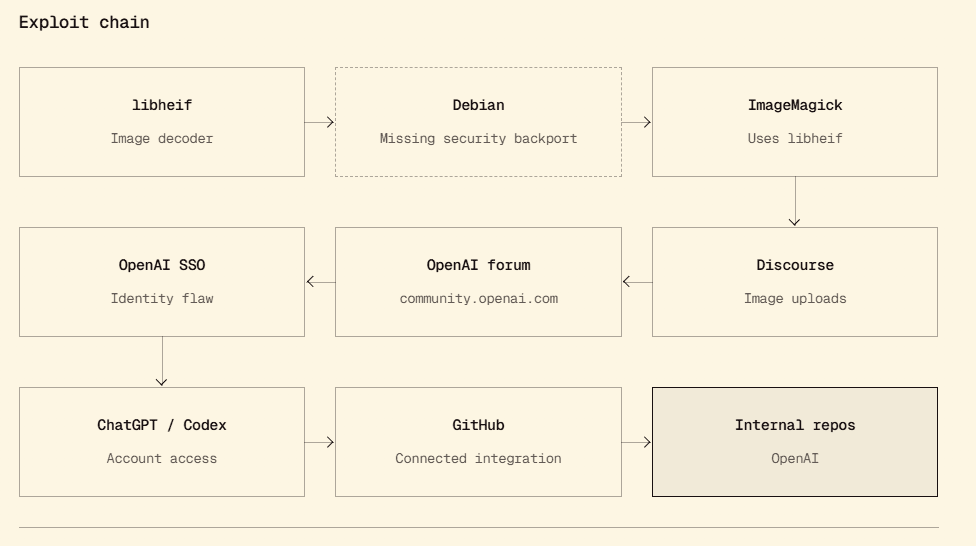
Security Affairs newsletter Round 595 by Pierluigi Paganini – INTERNATIONAL EDITION|Google Gemini also Broke Out of Its Test Environment|AI Helps Hackers Hijack OpenAI Staff Accounts Through a Forum|Brevo Supply-Chain Attack Infected Over 100,000 Websites|Gyazo Data Breach Exposes 23 Million User Records|RatHat Turns Android Accessibility Into an Attack Weapon|Check Point Fixes Critical CVE-2026-91843 Allowing Root Code Execution|OpenAI admits its models lie to cover their own mistakes|Cyberattacks on Oil Tankers Put Maritime Critical Infrastructure at Risk|SilkParasite Infrastructure Links SpiceRAT to Central Asian Targets|NightmareStresser Goes Offline in Global DDoS-for-Hire Crackdown|U.S. CISA adds Acronis Backup, Cisco ISE, and Google Pixel flaws to its Known Exploited Vulnerabilities catalog|Security Affairs newsletter Round 595 by Pierluigi Paganini – INTERNATIONAL EDITION|Google Gemini also Broke Out of Its Test Environment|AI Helps Hackers Hijack OpenAI Staff Accounts Through a Forum|Brevo Supply-Chain Attack Infected Over 100,000 Websites|Gyazo Data Breach Exposes 23 Million User Records|RatHat Turns Android Accessibility Into an Attack Weapon|Check Point Fixes Critical CVE-2026-91843 Allowing Root Code Execution|OpenAI admits its models lie to cover their own mistakes|Cyberattacks on Oil Tankers Put Maritime Critical Infrastructure at Risk|SilkParasite Infrastructure Links SpiceRAT to Central Asian Targets|NightmareStresser Goes Offline in Global DDoS-for-Hire Crackdown|U.S. CISA adds Acronis Backup, Cisco ISE, and Google Pixel flaws to its Known Exploited Vulnerabilities catalog|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 114

Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter REVSTEALER ramps up Breaking the Seal: Static Deobfuscation of JSCeal’s Compiled V8 Bytecode   GuardBreaker: Derailing AI-assisted malware analysis with a code comment   DPRK APTs: Ted backdoor and curlRAT target South Korean media and automotive […]

newsletter