
The Stegano exploit kit, also known as Astrum, continues to evolve, recently its authors adopted the Diffie-Hellman algorithm to hinder analysis.
The Stegano exploit kit made was associated in the past with a massive AdGholas malvertising campaign that delivered malware, mostly Gozi and RAMNIT trojans. Experts at TrendMicro also observed the exploit kit in the Seamless malvertising campaign.
“Astrum’s recent activities feature several upgrades and show how it’s starting to move away from the more established malware mentioned above. It appears these changes were done to lay the groundwork for future campaigns, and possibly to broaden its use. With a modus operandi that deters analysis and forensics by abusing the Diffie-Hellman key exchange, it appears Astrum is throwing down the gauntlet.” reads the analysis published by Trend Micro.

In March, the French research Kafeine reported the Stegano EK exploiting the information disclosure vulnerability tracked as CVE-2017-0022. Hackers exploited the flaw to evade antivirus detection and analysis.
A month later, the Stegano exploit kit was updated to prevent security researchers from replaying the malicious network traffic.
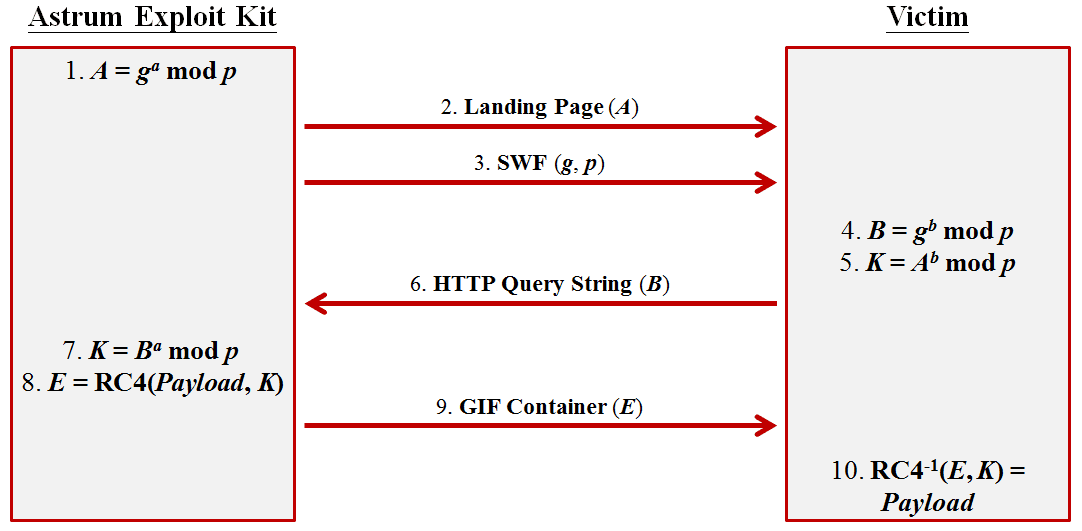
“We found that this anti-replay feature was designed to abuse the Diffie-Hellman key exchange—a widely used algorithm for encrypting and securing network protocols. Angler was first observed doing this back in 2015.” continues the analysis.
“Implementing the Diffie-Hellman key exchange prevents malware analysts and security researchers from getting a hold of the secret key Astrum uses to encrypt and decrypt their payloads. Consequently, obtaining the original payload by solely capturing its network traffic can be very difficult.”
According to the experts, the Astrum/ Stegano exploit kit includes exploit codes for a number of vulnerabilities in Adobe Flash, including the CVE-2015-8651 RCE, the CVE-2016-1019 RCE, and the out-of-bound read bug flaw tracked as CVE-2016-4117.
Experts highlighted that currently the Stegano Exploit Kit isn’t used to deliver malware and associated traffic is very low, both circumstances suggest we can soon observe a spike in its activity.
“It wouldn’t be a surprise if [Astrum/Stegano’s] operators turn it into an exclusive tool of the trade—like Magnitude and Neutrino did—or go beyond leveraging security flaws in Adobe Flash. Emulating capabilities from its predecessors such as fileless infections that can fingerprint its targets and deliver encrypted payloads shouldn’t be far off,” concluded Trend Micro.
[adrotate banner=”9″]
(Security Affairs – Stegano Exploit Kit, malware)
[adrotate banner=”13″]


