
Security Affairs
Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Sugar Ransomware, a new RaaS in the threat landscape

Cyber security team at retail giant Walmart dissected a new ransomware family dubbed Sugar, which implements a ransomware-as-a-service model. The cyber threat team at retail giant Walmart has analyzed a new ransomware family dubbed Sugar, which is offered through a ransomware-as-a-service (RaaS) model. Unlike other ransomware operations, Sugar ransomware appears to primarily focus on individual […]

sugar ransomware

Cyber security team at retail giant Walmart dissected a new ransomware family dubbed Sugar, which implements a ransomware-as-a-service model.

The cyber threat team at retail giant Walmart has analyzed a new ransomware family dubbed Sugar, which is offered through a ransomware-as-a-service (RaaS) model.

Unlike other ransomware operations, Sugar ransomware appears to primarily focus on individual computers instead of entire enterprises. The Sugar malware was first discovered in the wild in November 2021, it is a Delphi malware that borrows code from other ransomware families.

One of the most interesting components of the new malware family is the crypter that uses a modified version of RC4 algorithm and the reuse of the same routine from the crypter as part of the string decoding in the malware.

This suggests that the Sugar ransomware and its crypter were developed by the same team, another scenario sees the crypter that is being offered by a threat actor to a network of affiliates.

“The malware is written in Delphi but the interesting part from a RE perspective was the reuse of the same routine from the crypter as part of the string decoding in the malware, this would lead us to believe that they have the same dev and the crypter is probably part of the build process or some service the main actor offers to their affiliates.” reads the analysis published by Walmart.

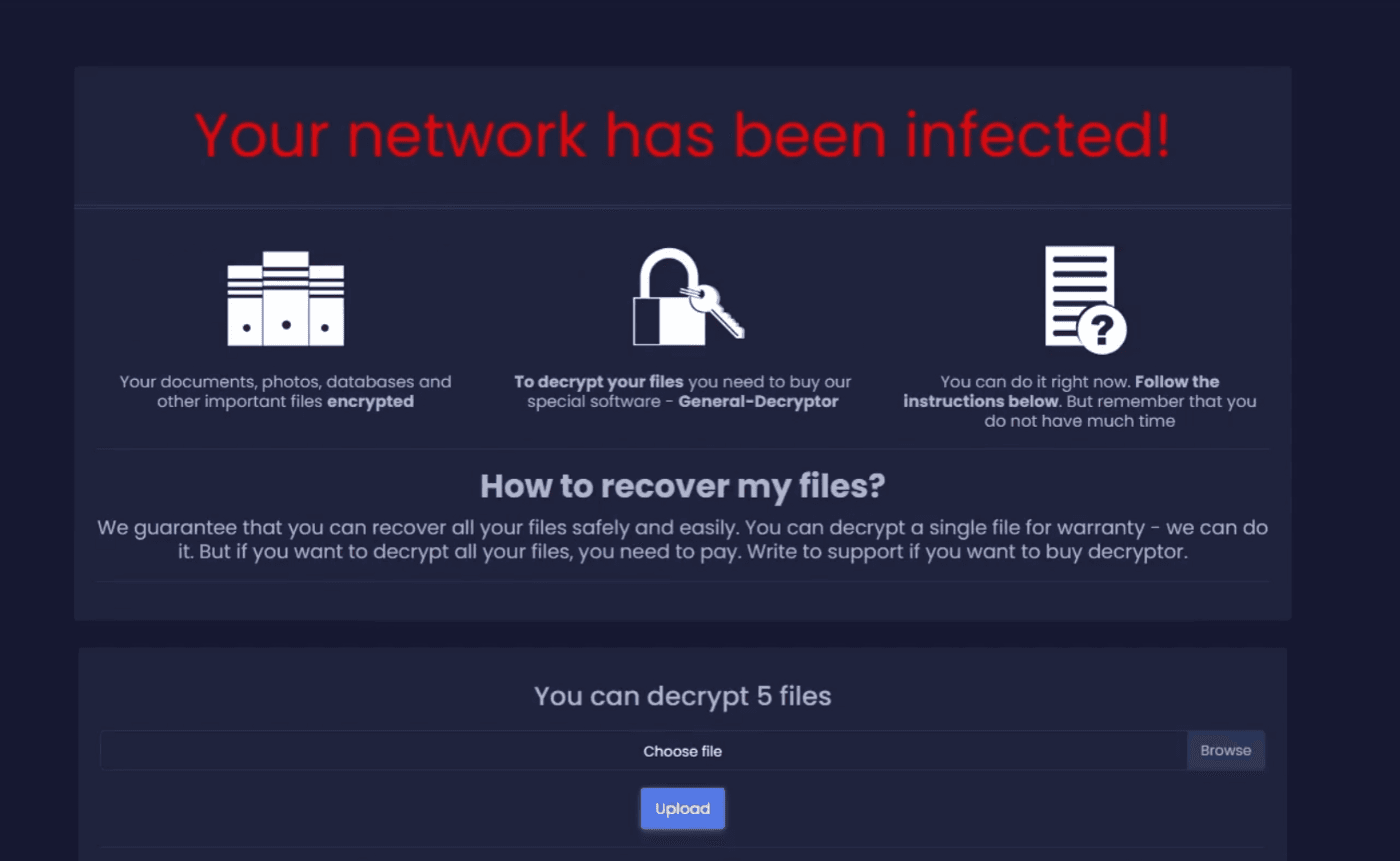
The experts also noticed some similarities between the ransomware of Sugar and the REvil‘s one, while the decryptor page is similar to the one used by Clop operators.

Other similarities were found by the experts in the GPLib library used for encryption/decryption operations.

sugar ransomware

The researchers also published Indicators of Compromise (IoCs) for this threat.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


