Security Affairs
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Previously undetected ThirdEye malware appears in the threat landscape

A new Windows information stealer dubbed ThirdEye appeared in the threat landscape, it has been active since April. Fortinet FortiGuard Labs discovered a previously undetected information stealer named ThirdEye. The malicious code is not sophisticated and can allow operators to steal various information from the infected machines. Fortinet started investigating the threat after the discovery of an […]

ThirdEye

A new Windows information stealer dubbed ThirdEye appeared in the threat landscape, it has been active since April.

Fortinet FortiGuard Labs discovered a previously undetected information stealer named ThirdEye.

The malicious code is not sophisticated and can allow operators to steal various information from the infected machines.

Fortinet started investigating the threat after the discovery of an archive file with a file name in Russian, “Табель учета рабочего времени.zip” (“time sheet” in English). The zip archive contains two files with .exe extension preceded by another document-related extension (double extension).

ThirdEye

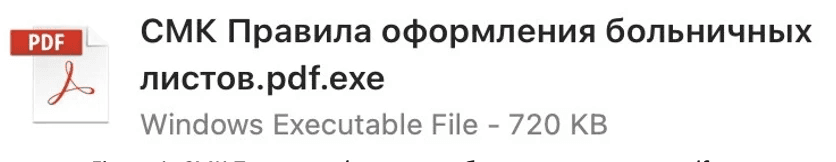
The malware was in an executable that masqueraded as a PDF file with a Russian name “CMK Правила оформления больничных листов.pdf.exe,” (“CMK Rules for issuing sick leaves.pdf.exe” in English)

Screenshot of Figure 1. CMK Правила оформления больничных листов.pdf.exe

Upon executing it, the ThirdEye infostealer harvests system information, and enumerates files and folders, running processes, and network information. Then the malware sends collected data to C2 server.

The malware name comes from the string “3rd_eye” which ThirdEye decrypts and uses, along with another hash value, as ID when connecting to the C2 server.

The second file in the .zip archive is “Табель учета рабочего времени.xls.exe”, which shares the same file name with the parent file. This file is a ThirdEye infostealer variant-

The investigation revealed that the first sample of the malware was uploaded to the file-scanning service VirusTotal on April 4th, 2023. 

This oldest sample was less efficient than recent samples and collected lesser information.

“Although there is no concrete evidence that ThirdEye infostealer was used in attacks, the malware is designed to collect information from compromised machines that is valuable for understanding and narrowing down potential targets. We believe this infostealer was designed for that purpose, and ThirdEye victims may be the subjects of future cyberattacks.” concludes the report. “Since most ThirdEye variants were submitted to a public scanning service from Russia, and the latest variant has a file name in Russian, the attacker may be looking to deploy malware to Russian-speaking organizations.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ThirdEye)