Security researchers at Core Security have discovered a dozen vulnerabilities in Trend Micro Linux-based Email Encryption Gateway.
Security researchers at Core Security have discovered a dozen flaws in Trend Micro Linux-based Email Encryption Gateway, some of them have been rated as critical and high severity. The flaws received the CVE identification numbers CVE-2018-6219 through CVE-2018-6230.
The most severe flaw could be exploited by a local or remote attacker with access to the targeted system to execute arbitrary commands with root privileges.
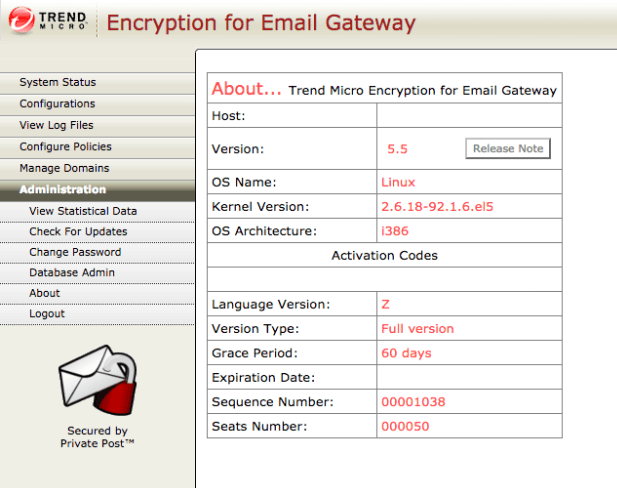
“Encryption for Email Gateway [1] is a Linux-based software solution providing the ability to perform the encryption and decryption of email at the corporate gateway, regardless of the email client, and the platform from which it originated. The encryption and decryption of email on the TMEEG client is controlled by a Policy Manager that enables an administrator to configure policies based on various parameters, such as sender and recipient email addresses,” states Core Security.
“Multiple vulnerabilities were found in the Trend Micro Email Encryption Gateway web console that would allow a remote unauthenticated attacker to gain command execution as root.”

The most serious vulnerability is CVE-2018-6223, it is related to missing authentication for appliance registration. Administrators can configure the virtual appliance running Email Encryption Gateway during the deployment process upon deployment via a registration endpoint.
The researchers discovered that attackers can access the endpoint without authentication to set administrator credentials and make other changes to the configuration.
“The registration endpoint is provided for system administrators to configure the virtual appliance upon deployment. However, this endpoint remains accessible without authentication even after the appliance is configured, which would allow attackers to set configuration parameters such as the administrator username and password.” continues the analysis.
The experts also discovered two high severity cross-site scripting (XSS) vulnerabilities, an arbitrary file write issue that can lead to command execution, am arbitrary log file locations leading command execution, and unvalidated software updates.
Remaining flaws discovered by the researchers include SQL and XML external entity (XXE) injections.
Affected Packages are Trend Micro Email Encryption Gateway 5.5 (Build 1111.00) and earlier, Trend Micro addressed ten of the vulnerabilities with the version 5.5 build 1129.
According to the report timeline, Trend Micro spent more than six months to issue the patches.
- 2017-06-05: Core Security sent an initial notification to Trend Micro, including a draft advisory.
- 2017-11-13: Core Security asked again (4th time) for an ETA for the official fix. We stated we need a release date or a thorough explanation on why after five months there is still no date defined. If there is no such answer we will be forced to publish the advisory.
- 2018-02-21: Advisory CORE-2017-0006 published.
Trend Micro confirmed that a medium severity CSRF issue and a low severity SQL injection vulnerability have not been patched due to the difficulties of implementing a fix.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Trend Micro Email Encryption Gateway, hacking)
[adrotate banner=”5″]
[adrotate banner=”13″]